The following things have been clear for a while:

  1. The three and four party models represented by the card schemes are in real danger of being disintermediated as mobile technology advances;
  2. The use of plastic will only begin to fade when consumers have a compelling reason to move, mobile payments alone is insufficient;
  3. Retailers are desperate to engage consumers much earlier in the buying process, as well as for a long time after it;
  4. Identity Management and Authentication will take their rightful place in payments and beyond; and
  5. The average consumer has no idea what they want

What has NOT been clear [to me anyway] is what will be the impetus for thing to actually change, and I never thought it would be a regulation.

But that is exactly what is happening here in the EU. Even a cursory examination of the Payment Services Directive 2 (PSD2) makes it clear that the established order is changing. It has already been adopted by the European Parliament, and adoption by the EU Council of Ministers is only a pending formality. Once published, each of the EU countries has just 2 years to write the Directive into their laws.

If you had to distill the PSD2 into its major players, they would be;

  1. Account Servicing Payment Service Provider (ASPSP) – Usually the banks, these guys will need to open up account data once they have received permission to do so from the consumer.
  2. Account Information Service Providers (AISPs) – Aggregators of data received from ASPSPs
  3. Payment Initiation Service Providers (PISPs) – Can initiate a payment, but can only provide a ‘Yes’ or ‘No’ in terms of funds availability.

It’s the AISPs that are truly the new guys on the block. Imagine it; a non-bank Third Party Provider (TPP) can, once properly vetted / ‘licensed’ request all the information from all of your banks / financial institutions and display it to you in a single location! The possibilities to money management alone are enormous, but it’s retail that will be the big winners. Well, some retailers.

The reason that retail and TPPs alike should be dribbling at the thought of this is that these centralised ‘Money Managers’ (MMs) are the perfect location to begin the buying process.

You want to buy a TV, so you open your MM app which has already gone through the effort to combine feeds from all of the following:

  1. Retailers – If retailers do not provide feeds of stock, deals, locations, terms and so on, these will not be presented to the consumer as an option
  2. Ratings & Reviews – Few people realise what goers into those 5 stars you see on Amazon and the like, but you’d be surprised how much influence they have
  3. Your Finances – No point looking if you can’t afford it

Then, once you have gone through a nice friendly wizard to narrow down what you are looking for, your MM goes out and looks for the best deal, AND offers you the best payment terms from all of your lenders. And the WAY you pay? What do you care, the MM has already determined the best way and took care of the detail?!

Those steps may not sound all that radical, but there are two incredibly important facts here:

1) the holder of your money has become far less relevant, so even the banks themselves are losing the Race to the Consumer, and

2) consumers will stop caring HOW they pay in terms of channel, making every other intermediary in the current payment ecosystem irrelevant.

This is what your money is, a stored value, why SHOULD you care if it’s direct debit, standing order, or branded card as long as it’s the best deal for you. It all comes back to you anyway.

[If you liked this article, please share! Want more like it, subscribe!]
This will be my first blog where I am going to a) plead ignorance; b) ask for your input, and c) actually listed to someone else’s opinion (potentially).

[gasp!]

I have just spent all day today going over parts of The Investigatory Powers Bill (IPB), the Regulation of Investigatory Powers Act (RIPA) of 2000, as well as listening to Theresa May’s statement on Parliamentlive.tv, all in an effort to find SOME evidence that it could “…allow Government to ban end-to-end encryption, technology powering iMessage and WhatsApp“.

OK, so that’s just according to The Independent, but The Guardian has their; “Investigatory powers bill: snooper’s charter to remain firmly in place“, The Telegraph has their; “Internet firms to be banned from offering unbreakable encryption under new laws” and so on.

All I could find in the IPB was this;

189 – Maintenance of technical capability

(4) The obligations that may be imposed by regulations under this section include, among other things—

(c) obligations relating to the removal of electronic protection applied by a relevant operator to any communications or data;

(e) obligations relating to the handling or disclosure of any material or data.

…as well as a reference to encryption as it related to RIPA, which states;

21 – Lawful acquisition and disclosure of communications data.

(4) In this Chapter “communications data” means any of the following—

(b) any information which includes none of the contents of a communication (apart from any information falling within paragraph (a)) and is about the use made by any person—

So, first my ignorance; I do not speak Governmental legalese, so I have no idea is the vagueness of this is just way of saying ‘we can do anything we want’, or it’s an established-by-precedent way of saying ‘this is all we can do’.

I have also not read the whole, thing, it’s 300 pages long and makes the PCI DSS look like the last Harry Potter book,

Which brings me to the second part; your input. There will be those who have read not only the IPB, but the RIPA, the Communications Data Bill of 2012, as well as the Data Retention and Investigatory Powers Act of 2014. You also are likely to fall [mostly] into one of only two categories; for, and against.

I would love to hear reasoned thoughts from both, or at least point me to an unbiased Cliff Note version of each!

Finally, listening to someone else’s opinion; anyone who has been nice / bored enough to read my blogs over the last 2.5 years will not have read even one where I was in any way unsure of my opinion / stance. Even when it comes to security (what’s the font for sarcasm?).

In this case, I am 100% on the fence (mostly because of 1. above), but partially because any talk of ‘investigatory powers’ or ‘interception of communications’ will have significant impact on privacy, and the implementation of my real interest; Identity Management.

While my thoughts on privacy itself are public record, the impact of what these Governmental powers will have on putting true Identity Management into effect are far from clear to me. There will be no secure mobile payments, no Internet of Things, and no hiding from your wife if there is something in the middle capable of ‘reading’ my communications. Not because I don’t trust the Government, but because anything THEY have access to will eventually be available to the bad guys.

We work within established rules of decency, they don’t (the bad guys that is).

Basically, please help, all comments / thoughts welcomed.

In a very interesting presentation at the 2015 ISC2 EMEA Congress in Munich, Dr Lucas Feiler posited that any big data analytics performed, whether internally or outsourced, is going to attract significant legal challenges related to privacy. And even if the challenges CAN be resolved, it will likely be in ways that make something of a mockery of the EU General Data Protection Regulation (GDPR)’s intent.

Getting around privacy regulations will involve token human interaction (i.e. smoke and mirrors) where none is desired. In areas that needs to be dominated by AI and the resulting automated decisions (insurance for example), adding the human element to avoid the appearance of prejudiced results will probably be standard until the algorithms become smart enough to be considered ‘reasonable’ (my absolute favourite legal term, right up there with ‘appropriate’).

Human interaction is not desired by those doing the analysis mind you, we may think otherwise.

While not in place …yet, the European Council aims for adoption of the GDPR in 2017 and have it in full effect after a “two-year transition period“. While 4 years may sound like a long time, when you consider the following statistics (taken from www.unifiedsocial.com) you can only imagine how difficult it will be to clean up the mess if organisations don’t start following the regulation now:

  • The data volume in the enterprise is estimated to grow 50x year-over-year between now and 2020
    o
  • 35 zettabytes (that’s 35,000,000,000,000,000,000,000 bytes) of data generated annually by 2020
    o
  • According to estimates, the volume of business data worldwide, across all companies, doubles every 1.2 years

Granted, the vast majority of this data will be in the form of cat videos and Kardashian tweets, but that still leaves an extraordinary amount of YOUR data sitting on servers just waiting to mined, manipulated, and analysed in ways we cannot even imagine. We cannot imagine them because they have not been INVENTED yet, and that’s the Holy Grail for any organisation, and the impetus behind big data analytics in the first place; How to manipulate the data they have into the development of new revenue streams.

To put that another way; How to take the data they have on you already and present it back to you in a way that makes you spend more money.

I’m actually not against this per se, Amazon are already doing a mild version of it with their “Frequently Bought Together” and “Customers Who Bought This Item Also Bought” sections, but can you imagine how much data they have on their more than 1.5 MILLION servers across 17 global regions?

The card brands and Facebook can predict within a two week window whether or not you’re going to get divorced, how much other data do THEY have? Or Google?

But can the GDPR actually make a difference? Probably, it has a VERY big stick, and you know how lawyers love their class action suits!

Look at GDPR CHAPTER II, PRINCIPLES, Article 5 – Principles relating to personal data processing:

Personal data must be:

(a) processed lawfully, fairly and in a transparent manner in relation to the data subject;

(b) collected for specified, explicit and legitimate purposes and not further processed in a way incompatible with those purposes; (…);

(c) adequate, relevant and not excessive in relation to the purposes for which they are processed (…);

Etc…

…and now CHAPTER VIII, REMEDIES, LIABILITY AND SANCTIONS, Article 79a – Administrative fines:

The supervisory authority (…) may impose a fine that shall not exceed 1 000 000 EUR or, in case of an undertaking, 2 % of its total worldwide annual turnover of the preceding financial year, on a controller or processor who, intentionally or negligently:

(a) processes personal data without a (…) legal basis for the processing or does not comply with the conditions for consent pursuant to Articles 6, 7, 8 and 9;

If you LOSE personal data the fines can be a much as 5% of worldwide annual turnover.

Will that make a difference?

I hope so.


If the answer is yes, you have clearly not learned any lessons from years of regulatory compliance, breach headlines, every security best practice, or basic common sense. And if you continue to do nothing, for whatever the reason, you likely deserve the bad things that happen to you.

Yes that’s harsh, but non-compliance is all so unnecessary. Just like PCI, nothing the PSD2 mandates is something you should not have been doing a long time ago, and if 2 YEARS is not enough time to fix what’s broken in your organisation, please let me know so I can stop doing business with you.

If you’re a financial institution, did it not occur to you to stay up to speed with the latest and greatest advances in access control? Data classification and meta tagging? Did not the FIRST version of the PSD have enough hints that the ever-worsening threat landscape was only going to increase the security and privacy burdens?

Worse than this are the two major offenders; 1) Payment Service Providers (PSPs) who thought that they were somehow immune to regulation because “it’s not OUR data”, and 2) the FI’s who used them because they thought they could outsource the responsibility.

Yes, security come at a cost, and very little of that expense will ADD to your bottom line, but if it’s an ROI you’re looking for, how about staying is business? Between PSD2 sanctions and potentially EU General Data Protection Regulation (GDPR) fines/sanctions, and maybe even PCI fines if it’s cardholder data you lose, I would say your responsibility is clear.

But it’s not all doom and gloom, the path towards compliance is actually very simple. Not easy, simple.

First, get the CEO and/or Board of Directors involved. if they don’t care, no-one else will, and any project to achieve ANY form of compliance will either fail out of the gate, take twice as long, or cost twice as much. As I’ve said too many times now;

“Let’s be very clear; The CEO sets the tone for the entire company: its vision, its values, its direction, and its priorities.  If the organisation fails to achieve [enter any goal here], its the CEOs fault, and no-one else’s.”

Second, run a risk assessment to determine 3 things; 1) what business assets and processes are affected, 2) what are the gaps between current and required capabilities and 3) how much should you spend to fill those gaps.

In parallel with the risk assessment, fix your documentation!! The cheapest and most important facet of every security program is the one most ignored, thereby rendering everything else you do somewhere on the scale of sub-optimal all the way to completely ineffectual.

Third, do NOT do this just to achieve PSD2 ‘compliance’, do it for ALL aspects of your business, and do it once. Done properly, any progress toward any form of regulatory compliance becomes a standard operating procedure, and eventually the ages-old cliché; business as usual. Anything other than this was wasted effort irrespective of it’s intended goal.

You wouldn’t ask your doctor for a temporary fix would you, security is no different?

In the end, you really only have 2 choices; throw a patch on a gaping wound and hope that you have implemented enough smoke and mirrors to stay under the radar, or do things properly and avoid the worst of the fines regardless of how long it takes to get compliant. While that sounds somewhat counterintuitive, the regulators do not WANT to fine anyone, but if data is lost, it will be the bullshit artist who will be hurt the most.

Truth be told, this post could be titled; ‘The Top Roadblock to Compliance, and The Other 9 That Result From It”, but per the excellent advice from a blogger far better than I “You can’t [stop readers cold] if you use cute, clever or confusing headlines.” I’m keeping it simple.

So what is this offending roadblock?

1. Lack of Management Buy-In

Sounds simple, in fact, it sounds like a cliche, and above all, it does not sound anywhere near as important as I’m making it out to be. But let me ask you this; If your manager doesn’t care about something, how much do YOU care about it?

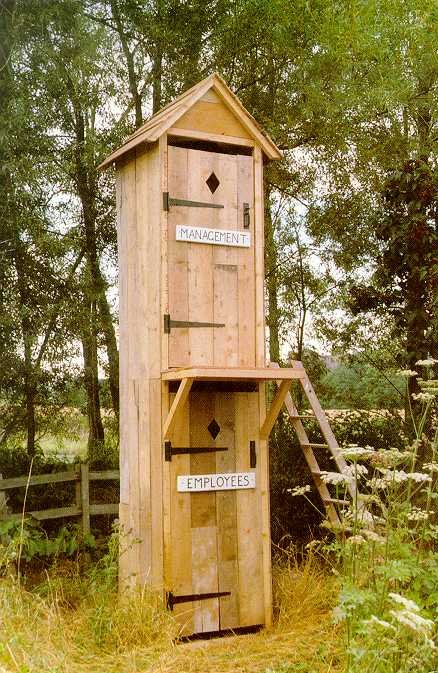
Now extrapolate that from the CEO all the way down and you get something like this;

Management

If the CEO makes it clear that they don’t care about PCI, how much traction do you think achieving compliance is going to get? The project gets handed to the IT Manager (because it’s clearly an IT problem not a business one, right?), and PCI will receive no attention, very limited budget, and no respect.

That is, until they get breached and fined for the equivalent of gross negligence, and then the IT Manager gets blamed for slacking. Sounds familiar?

The CEO, as well as senior management, control the culture, and that culture had better include the importance of cybersecurity.

Let’s be very clear; The CEO sets the tone for the entire company; its vision, its values, its direction, and its priorities. If the organisation fails to achieve PCI compliance, it’s the CEOs fault, and no-one else’s.

And now for the other 9…

2. No Perceived Return on Investment (ROI)

While very closely tied to the 1st reason, this is distinct because it’s clear that few have accepted that there are actually benefits of PCI compliance (see Why PCI Isn’t ALL Bad). So even if the CEO does pretend to care, few will get behind the process in any meaningful way. Nor will they bother trying to fit PCI into their existing security program, which is the only way it makes sense.

3. No Dedicated PCI Project Manager

PCI compliance, like all security, is eventually a process, but achieving it for the first time should be a project with a dedicated internal resource. Ideally, that resource has nothing else to do except PCI, but that’s rarely practical. So until compliance is achieved, they will need considerable support from management, and some of their more mundane duties re-distributed.

4. Choosing the Wrong QSA 

Per my white paper on Selecting the Right QSA for Your Business, the choice of an assessor is extremely important. The right one can help you deal with almost all of these roadblocks, the wrong QSA may be the roadblock. It’s probably in your best interests to bring a security expert in first to prepare your security program and infrastructure for the QSAs visit. At the same time helping you to make not only PCI, but your entire security programme sustainable – and just as importantly – cost effective. And above all, appropriate to the value of the data to your business.

5. Thinking Policies & Procedures are Just Paperwork

Odd as it sounds, without solid documented and enforced policies, standards and procedures (Policy Set), there is no real way you can have the culture of security necessary to achieve the company wide backing necessary to run an effective PCI project. The Policy Set is a corner-stone of your security program and should received its due.

6. No Standardisation

This is a very broad subject, and includes configuration standards, change control, monitoring, patch management, the SDLC, vulnerability management etc. The PCI DSS allows sampling of systems during validation, but this must be earned. Without standardisation, there can be no sampling as there are no systems created and maintained identically.

7. No Centralisation

How organisations manage often hundreds of devices without some form of centralised management is beyond me. I have to assume it’s not done well. The QSA also has a very hard time granting the privilege of sampling if you cannot show centrally HOW you keep the systems the same. There are plenty of tools out there, and the benefits of them go way beyond PCI compliance.

8. Not Knowing Where to Start

At first this may seem obvious, and perhaps a little redundant, but bear with me. I have had a lot of experience with this little roadblock, so I know just how difficult it can be to overcome. The answer – as it was for me – is simple; Ask someone. Your QSA should be able to take you all the way through this process relatively seamlessly, but if you don’t have one yet, ask someone who has already achieved compliance for their organisation. I personally know dozens of people who are more than happy to spend time with PCI novices and share their experience and guidance. This is one of the easiest roadblocks to overcome if you keep your ego or shyness out of play.

9. “But we’ve always done it this way!”

Perhaps the most irritating phrase in the English language – with the possible exception of “What are you thinking?”, especially for a consultant. The business wants things to stay the same, they want the same access they’ve always had, and they want the same data. The fact remains that the vast majority of business processes have very short shelf-lives, so they should be reviewed regularly, and access to in-scope systems or data justified. I’ve found that adding PCI compliance expenses to their cost centres tends to get their attention.

10. No Budget

Not much you can do about this one, but it’s certainly worth trying to re-iterate that the security controls should be in place anyway, and that they fall firmly in the good practices introduced in my The 6 Security Core Concepts.

I didn’t know how to blog until I asked my wife, and I have no idea how to read legal-ese so I ask my Sister. If you want to be PCI complaint, or even better, be secure AND PCI compliant, ask someone who’s done it.

[If you liked this article, please share! Want more like it, subscribe!]