Over the last 6 months since leaving a 12+ year career at one company, my thoughts come consistently back to one concept; innovation. Making positive change in terms of process and efficiency has always been a passion of mine. Nothing is perfect, and anyone using the phrase; “We’ve always done it that way!” should be fired immediately for gross misconduct.

In much the same way that to someone with a hammer every problem looks like a nail, my natural inclination as a security ‘expert’ is to assign the lion’s share of importance to my area of expertise. While I most likely go too far in this, I think that I have at least some justification for my assertions, if only in the context of this blog.

Innovation is defined as; The act of introducing something new. This is therefore one of the most critical concepts for the human race since it first achieved sentience (couldn’t use the word ‘intelligence’, I think that’s still pending). Whether you believe that was millions of years ago, 6,000-ish year ago, or it was a present from aliens, the speed with which we evolved from hunter-gatherers into what we are now is astonishing (couldn’t use the word ‘civilised’ either, and for the same reason). In just the last 100 years or so we’ve gone from the first flight to the moon, and from computers the size of a room, to mobile devices with more computing power and capacity per unit than existed on the planet just 60 years ago.

All of this was done with one thing as the foundation; information. Yes, that information must be correctly applied to become knowledge – and hopefully in time, wisdom – but everything that has ever been invented, and WILL ever be invented, has information at it’s core. Invention starts with a need, and it does not matter what that need is, someone will feel the urge to fill it. Only a few people create things of no use (we’ll leave Apple and Modern Art out of this), they do it to make money, make a difference, or better the human condition.

The need, in and of itself, is a sort of information; how to take an idea and make something out of it is information; how to build / market / sell / distribute / improve the idea is information; and yes, how to USE the results of the idea is also information.

So why isn’t information better protected?

Why isn’t information seen at the definitive crown jewels in EVERY organisation, especially now that almost every aspect of business is digital, and online? Why don’t CEOs include those in CHARGE of protecting information in the process of business transformation and innovation?

Can’t answer those questions, I’m not smart enough, but seeing as I’m a security expert the why is irrelevant, it’s my job to ‘just get it done’. But that’s the challenge, unless the people ultimately responsible for innovation within a business understand and care about this concept, no-one else is going to care (yes, I’m blaming the CEO …again).

There is an ages old concept in information security; that of Confidentiality, Integrity, and Availability. Some say it’s obsolete and needs refreshing, others try to change the names or add a 4th so that they can be seen to be radical thinkers, but the concept is every bit as valid as it’s ever been:

Confidentiality: If everyone has the information you have, you’re probably not innovating, you’re doing what everyone else is doing. Maybe you’re doing it slightly better than everyone else, but you aren’t going to stay in the lead for long.

Integrity: Not much point innovating if you’re doing it for the wrong reasons, in the wrong place, at the wrong time, or badly. If your information is not accurate and relevant it’s just data.

Availability: You can have all the information in the world, but if you can’t get to it WHEN you need to get to it, it as much use as a politician.

The whole point of IT Security is to take care of confidentiality and integrity, IT Operations takes care of the availability, but it’s the combination of IT Operations,  IT Security and the BUSINESS side to put information into context for ongoing innovation.  That’s what the Governance committee is supposed to be doing; take a business need, help gather the necessary information to devise a solution, measure the business risk, and either move forward with the solution, or move on to the next.

Big data, data mining, predictive analytics and even the much mis-understood ratings and reviews fields would not be experiencing exponential growth if information was not seen as crucial to maintaining competitive advantage. That’s probably why it’s almost incomprehensible to me that organisations don’t take information security more seriously.

Almost.

I provided my first PCI guidance way back in 2005, and my first on-site assessment was in 2006. Since then I have performed dozens of on-sites across the globe, my last one in 2009. Until December 2012, I ran teams that delivered PCI assessments across EMEA and APAC, all of whom followed a proven methodology that took all the guesswork out of how to achieve compliance, and STAY compliant.

Over the last few months, my changed circumstances have led me back into the PCI weeds, and frankly, I am more than a little disappointed. The payment card industry is no closer to ‘getting it’ than they were 8 years ago, and the guidance provided by a significant portion of PCI professionals leaves a lot to be desired.

After >8 years, the industry SHOULD be integrating their PCI assessment processes into some form of overarching security framework, re-certification SHOULD be nearing business as usual, and QSA quality should have improved.

They’re not, it’s not, and it hasn’t respectively.

I have written several articles on the major issues with the DSS, and what to do about them, I have stated more times than I probably should that the problems begin and end with the CEO, and I have repeatedly quoted my tag-line;

“Security is not easy, but it can be simple.”

I even wrote white papers on How to Sell Security (and therefore how to BUY security), and Selecting The Right QSA For Your Business in an effort to help standardise and optimise the most important step towards compliance; asking for help.

For some reason this has not had the industry changing effect I had expected. Surely my 18 subscribers – 4 of whom are family members – should have had a bigger impact than this!? [uncomfortable silence]

I have said for a few years now that I should put all of my experience into a PCI self-help book. Well, now I’m going to. Not all at once mind you, I’m going to write each chapter as a stand-alone ‘white paper’ over the course of the next few months, and will request your feedback on each. When they are as polished as they are going to be, maybe I’ll try to get it published, but I’ll still give it all away here on my blog.

I will also include any tool-sets I use to conduct an assessment (plus samples / examples), and I will provide options for free-ware / cheap-ware tools that I have seen be of some use. I will NEVER recommend anything, and only offer up options upon which you must perform your own due diligence. I may highlight my OWN preferred solutions, but the choices, and therefore responsibility, will always be yours.

These are the chapters I have in mind, and in this order:

  1. So You Want To Be PCI Compliant? (a.k.a. Buy Nothing Until You Read This!)
  2. Biased Perspective – What The PCI DSS Is, And What It Can Never Be
  3. Prepare Your Organisation (i.e. Your CEO) For The Assessment
  4. The Assessment Pre-Requisites
  5. Report on Compliance Executive Summary – If You Can’t Write This, Start Again
  6. DSS Requirement 1 – Networking Stuff
  7. DSS Requirement 2 – System Configuration Stuff
  8. DSS Requirement 3 – Encryption Stuff
  9. DSS Requirement 4 – More Encryption Stuff
  10. DSS Requirement 5 – Anti-Virus Stuff
  11. DSS Requirement 6 – Vulnerability Management, Change Control, Secure Coding Stuff
  12. DSS Requirement 7 – Access Control Stuff
  13. DSS Requirement 8 – Password Stuff
  14. DSS Requirement 9 – Physical and Back-Up Stuff
  15. DSS Requirement 10 – Logging Stuff
  16. DSS Requirement 11 – Testing Stuff
  17. DSS Requirement 12 – Policy, Training & Incident Response Stuff
  18. Compensating Controls
  19. Validation and Evidence Collection
  20. The Holy Grail of Security, Continuous Compliance Validation
  21. The Future Of PCI – Things To Bear In Mind

There are entire companies founded on, and still making fortunes from, PCI. I can, quite literally, thank PCI for my entire career in security (well, that and Windows), but it’s time we put PCI into the proper perspective, and start spending that money on the only thing that makes sense; staying in business responsibly.

If anyone would like to collaborate of any of these chapters, feel free to reach out to me. Especially encryption!!

PCI DSS

Once in a great while, a phrase comes along that immediately sparks a thousand thoughts in your head.  It does’t matter if the thoughts are even relevant to the context in which you heard the phrase, the thoughts are there.  Clearly my written English will give this poor justice, and as my Sister is always kind enough to point out; I’ve never met a grammatical error I didn’t like.

Unfortunately the phrase ‘strategically intelligent mistakes‘ is not mine, it’s Accenture’s, but was brought to my attention in a pending article by Peter Livingstone, a Publisher at Financier Worldwide. I will be ‘advertising’ this article when it comes out so that my enormous following can enjoy it.  I’m fairly sure my 18 subscribers will make all the difference to its success.

Accenture’s context is; “Some companies have recognized that they can allow innovation teams to make strategically intelligent mistakes within a clearly understood governance framework. This, in turn, enables a culture that not only tolerates risk but also embraces failure as an integral part of the innovation process.”

Which is perfect for the purposes of this blog, (and my last one on Why Everyone Should Start a Business) because it’s very much the thought of failure that prevents so many good ideas from becoming reality, or causes thoughts to die on the vine. That, and having no idea where to start, but that’s blodder for another time.

Whether the idea is for a start-up, a new service line, or an improvement on something that already exists, fear of failure / ridicule / loss of respect, or any number of fear-based de-motivators prevent those ideas from being freely expressed. The only truly bad idea in business is one that never see’s the light of day. Sure, it might fail, fail spectacularly even, but no-one has just one idea, so the next one will have the benefit of experience for the creator, and everyone around them.

Thomas Edison, arguably the most famous inventor in recent history, failed over 3,000 times to invent the lightbulb (though he certainly didn’t phrase it that way).  My favourite quote of his; “Many of life’s failures are people who did not realize how close they were to success when they gave up.”

You do not have to be an entrepreneur and start your own business to make a significant impact with your ideas, there are plenty of examples of an ordinary individuals’ idea making significant positive impact on an organisation. It is the CEO who ultimately holds the key to how ideas are received, and whether or not his/her people feel as though their ideas are welcomed, regardless of the possible outcome.

A recurring theme in my blogs is; “Let’s be very clear; The CEO sets the tone for the entire company: its vision, its values, its direction, and its priorities.  If the organisation fails to achieve [enter goal here], it’s the CEOs’ fault, and no-one else’s.”

In Accenture’s article, there is this wonderful paragraph; “For instance, a large advertising agency awards a quarterly Heroic Failure trophy to recognize clever, unproven ideas that may not work out in practice, but nevertheless demonstrate creative risk taking. And an online payroll provider offers $400 to the winner of its Best New Mistake award, which goes to an employee who made a mistake but learned from it—and, in doing so, helped other employees avoid similar mistakes. The idea behind both awards is to support creativity by encouraging openness about errors and rewarding those who genuinely learn from their failures.”

Can you imagine working for an organisation that rewards and encourages you  regardless of your mistakes.  No, neither can I, but it’s a very pleasant thought isn’t it?

========================

Update 14-Oct-13 15:09: My thanks to Jon Hawes for pointing me at this article; http://blogs.hbr.org/2013/09/how-i-got-my-team-to-fail-more/


Now that I’ve had the opportunity to review the full draft standard, it’s clear that there’s very little that’s difficult for you to achieve in the short term if, and I mean IF, you were doing PCI properly from v2.0 onwards. The majority of the changes are simple clarifications, and if your QSA was doing their validation and QA correctly, you would already be doing 99% of them.

That’s really all v3.0 is; a closer approximation to the Report on Compliance (RoC) scoring mechanism that’s been around for years. I understand the clarifications and the guidance are supposed to bring everyone’s understanding of the INTENT of each requirement into closer alignment, but all that does is reflect very badly on the current quality of the QSAs and the available guidance.  The corollary is that the QSA and ISA training needs some serious attention, and the DSS needs to focus less on the detail, and more on the senior management buy-in.

I also understand that it is VERY difficult to make dramatic changes to a standard when organisations have already invested significant capital and resources into achieving compliance. But even the SSC made it VERY clear from the beginning that the DSS was a MINIMUM set of controls around a single form of sensitive data, and should not be seen as a security programme that meets the entire business’s needs (per the PCI DSS v3.0: “PCI DSS comprises a minimum set of requirements for protecting cardholder data…“).

So why aren’t the changes in v3.0 more significant?  Or more in line with good practices?  I don’t really have a constructive (a.k.a. non-soapbox) answer to that, so I’ll focus on what I perceive to be the major flaws.

Here’s my Top 3 Flaws:

Governance:  This has as many definitions as there are people defining it, but in the end it’s very simple; Governance is the Business side and the IT side having conversations.  Business has the requirements (growth, profit, transformation etc.), IT has the enablement, and the organisation as a whole moves forward appropriately. Nothing should happen in an organisation outside of this framework if the business wants to grow/innovate/adapt effectively (for more see Security Core Concept 4: Governance & Change Control and Security Core Concepts: Tying it All Together)

Guess how many times the word ‘Governance’ (or equivalent) appears in v3.0?

Not once.

Risk Assessment (RA): The whole business/IT/security life-cycle starts with a risk assessment.  The business wants something, the RA determines the balance of risk/reward, and you move on to implementation if the balance is favourable.  The DSS calls for a RA, but it’s still woefully understated, and stuck down in the ‘paperwork’ section (Section 12).  This should have been performed even before you chose a QSA, should be intrinsic to services you eventually receive from them, and should have driven all purchase(s) of technology used to achieve both compliance and security in general (for more see Security Core Concept 1: Risk Assessment / Business Impact Analysis).

The Risk Assessment even had its own Special Interest Group (SIG) to improve the quality of the guidance, but the results were so watered down as to be ineffectual.

Sampling: MUCH better explanation than previously, but it’s missing the most important phrase; “There is no sampling in PCI DSS validation unless the client can reasonably demonstrate how all ‘like’ systems are configured and maintained identically, managed and monitored centrally, and are promoted into production through a well defined and documented  process.”

For too long sampling has been seen as a right, it’s not, it’s a privilege (like spandex). Saying “Sampling is an option…” is not enough to avoid clients demanding ‘pragmatism’ from their QSAs in the ‘this-is-too-difficult’ sense of the word.

I have so much more to say, and some of it is actually positive (like pushing policy enforcement validation), but I’ve already overrun my self-imposed word limit.

Finally, every organisation that relies totally on PCI for their security deserves to be hacked – sorry, but you do – but the SSC and the card brands still have an obligation to do more to evolve the standard into something that can be integrated seamlessly into an established, and comprehensive good-security-practice framework.  By the time the DSS catches up with the real world of security, payments will have moved on from payment cards.

Just ask any non-QSA security expert what you should be doing with your IT budget, I’ll bet it’s not PCI compliance.

[If you liked this article, please share! Want more like it, subscribe!]

According to statistics that I’ve just made up, less than [cough]% of all breaches are the result of a determined / planned attack, the remaining [mumble]% are the result of inadequate security of one sort or another.

The second sort is the overwhelming majority, but yes, I do need to start doing proper research.

My proposition is simple:

  1. CEO doesn’t seem to care = no-one else cares;
  2. CEO ignores security = everyone else ignores security;
  3. CEO is passive-aggressive and devoid of  charisma =  s/he will surround themselves with talentless sycophants…

…you get the point.

I am always amazed that the kind of people who have the ability to either raise themselves to the top position, or start their own company, are often completely incapable of using their enormous influence to an end that has value and meaning.  Well, beyond the self–serving kind anyway.

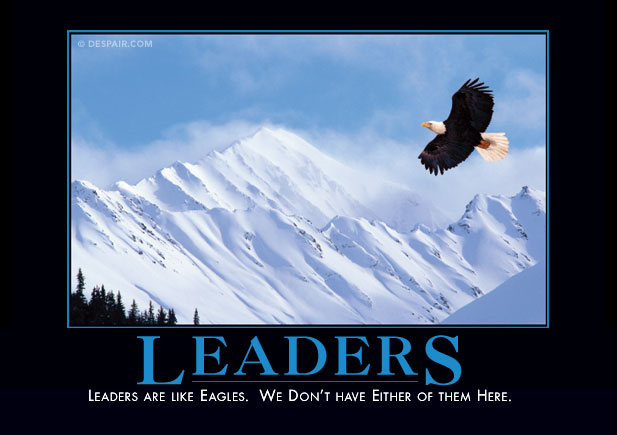
My absolute favourite Demotivator (www.despair.com) is this one;

leadersdemotivator

Like most humour, it’s only funny if it’s at least partially true. Sadly, this is the case for many organisation in terms of leadership in the realm of security.

As I have stated WAY too many times now;

“Let’s be very clear; The CEO sets the tone for the entire company: its vision, its values, its direction, and its priorities.  If the organisation fails to achieve [enter any goal here], it’s the CEOs fault, and no-one else’s.“

I can think of one very good example in my own experience where the CEO actually took time out of their busy schedule to RUN the PCI assessment every year.  Of course she delegates the detail to her team, but she remains the focal point for communication and issues, and gets her hands dirty every day ensuring that her entire company takes security as seriously as she does.  The result is that they achieve compliance every year with a minimum of ADDITIONAL effort beyond their business as usual processes.

Unfortunately in this case her chosen consulting company also sold her a bunch of their crappy products that caused never-ending grief, but that’s life.

Despite all of the articles I’ve written on a variety of subjects, I really only have one goal for this blog; to change the perception of what security is, and what it can do for a business.

Security started out on the wrong foot by being lumped in with IT, who were already seen almost as a necessary evil. I guess it’s kinda like Scotty in Star Trek, he has saved their skins a thousand times by “giving ‘er all she’s got” but it’s always Kirk who gets the glory.  And yes, I’m very aware I just completely stereotyped myself.

In reality, no other department in an organisation has a better idea of exactly HOW they do business.  Every server, laptop, mobile phone (pre-BYOD), database and application is maintained by IT, and all of THAT is under the purview of security whose job it is to make sure it stays available and accurate.  But that’s just the beginning, it’s what the security folks can do WITH that knowledge that brings the real benefits (see How Information Security Enables Transformational Change for one such example).

The challenge I face however, is that the benefits will only ever be achieved if the CEO supports it.  Nothing happens without them, and seeing as I’m just in security, you can imagine how many CEOs I get in front of.

Still, a goal is a goal.

[If you liked this article, please share! Want more like it, subscribe!]