
[blank] as a Service. There are so many XaaS services available now that we are running out of letters:

  • AaaS – Authentication as a Service
  • BaaS – Back-End as a Service
  • CaaS – Communication as a Service`
  • DaaS – Desktop or Data as a Service
  • EaaS – Encryption as a Service
  • FaaS – Failure as a Service [I know, couldn’t believe this one myself]
  • …and so on.

As much as I have an issue with buzz-words and inventing acronyms, I cannot deny the trend that; Unless it’s a core function, don’t do it yourself.

Retailers should outsource payment acceptance, insurance companies should outsource cyber due diligence, and every business should outsource some of its security risk management.

Sure you can change the oil in your own car, you may even be able to perform some basic plumbing, but why would you? There’s an excellent chance that a professional can do it better, and in the long-run cheaper, than you. What’s more important; saving money, or saving your time? I guess the answer is different for everyone, but a business does not have the luxury of experimentation to the degree we do. False economy, while relatively trivial for us, can be make or break to a business.

I see a time where the economies of scale, combined with the abundance of competition will enable service providers to give far better service at a much lower price-tag that you could possibly hope to achieve in-house. Doing one thing and doing it well should automatically provide the necessary scalability of service, appropriate innovation and business transformation capability necessary to run a competitive venture in the 2010s and beyond.

Even in the cybersecurity industry, there is significant confusion on how to choose the right vendor or technology, and this will only increase exponentially in the era of The Outsourcing of Everything. Inevitably there will come along a new type of service provider; the Service Provider Integrator. In the same way you cannot manage your security if you have 15 different management stations, you cannot run your business if your service providers are not performing seamlessly, and in full support of your business goals.

In the Information Age, where entire businesses can be run in the virtual world, a competitive edge lasts weeks, not years, and only the organisations who can effective balance risk and innovation, and then transform their business processes in support of that innovation, will succeed. And with everything outsourced, only the companies who are best able to chose, then integrate the most effective and flexible services, can hope to compete. The best Service Provider Integrators will be able to create entire white-labeled businesses from any concept.

In one of my earlier blogs; How Information Security Enables Transformational Change, I made the statement; “Information in context is knowledge, success however is in the correct application of that knowledge.”. The drive towards specialisation will accelerate in every service to be provided. It will be the organisations that are best able to correlate both the management information gathered over years of providing a specific services to multiple organisations, along with the ability to apply those skills to prospective clients, who will run away with the business. This will eventually create new Googles and Amazons, but they are where they are for a reason;

Good service.

[If you liked this article, please share! Want more like it, subscribe!]

========================

Update 22-Oct-13 09:23: Don’t normally add bad language to my posts, but this is too funny not to; www.foaas.com. My thanks to Steve R!
Truth be told, this post could be titled; ‘The Top Roadblock to Compliance, and The Other 9 That Result From It”, but per the excellent advice from a blogger far better than I “You can’t [stop readers cold] if you use cute, clever or confusing headlines.” I’m keeping it simple.

So what is this offending roadblock?

1. Lack of Management Buy-In

Sounds simple, in fact, it sounds like a cliche, and above all, it does not sound anywhere near as important as I’m making it out to be. But let me ask you this; If your manager doesn’t care about something, how much do YOU care about it?

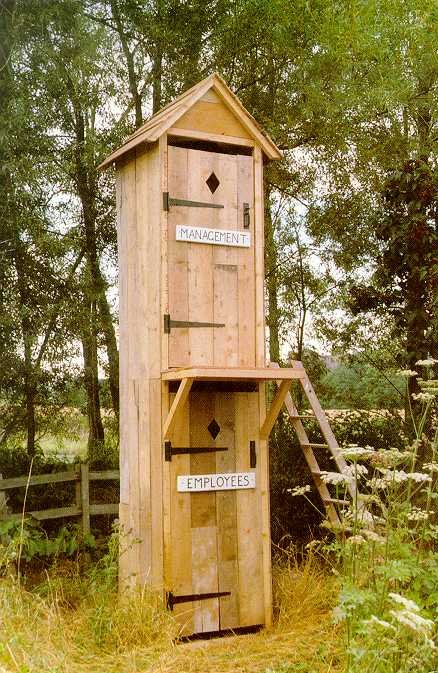
Now extrapolate that from the CEO all the way down and you get something like this;

Management

If the CEO makes it clear that they don’t care about PCI, how much traction do you think achieving compliance is going to get? The project gets handed to the IT Manager (because it’s clearly an IT problem not a business one, right?), and PCI will receive no attention, very limited budget, and no respect.

That is, until they get breached and fined for the equivalent of gross negligence, and then the IT Manager gets blamed for slacking. Sounds familiar?

The CEO, as well as senior management, control the culture, and that culture had better include the importance of cybersecurity.

Let’s be very clear; The CEO sets the tone for the entire company; its vision, its values, its direction, and its priorities. If the organisation fails to achieve PCI compliance, it’s the CEOs fault, and no-one else’s.

And now for the other 9…

2. No Perceived Return on Investment (ROI)

While very closely tied to the 1st reason, this is distinct because it’s clear that few have accepted that there are actually benefits of PCI compliance (see Why PCI Isn’t ALL Bad). So even if the CEO does pretend to care, few will get behind the process in any meaningful way. Nor will they bother trying to fit PCI into their existing security program, which is the only way it makes sense.

3. No Dedicated PCI Project Manager

PCI compliance, like all security, is eventually a process, but achieving it for the first time should be a project with a dedicated internal resource. Ideally, that resource has nothing else to do except PCI, but that’s rarely practical. So until compliance is achieved, they will need considerable support from management, and some of their more mundane duties re-distributed.

4. Choosing the Wrong QSA 

Per my white paper on Selecting the Right QSA for Your Business, the choice of an assessor is extremely important. The right one can help you deal with almost all of these roadblocks, the wrong QSA may be the roadblock. It’s probably in your best interests to bring a security expert in first to prepare your security program and infrastructure for the QSAs visit. At the same time helping you to make not only PCI, but your entire security programme sustainable – and just as importantly – cost effective. And above all, appropriate to the value of the data to your business.

5. Thinking Policies & Procedures are Just Paperwork

Odd as it sounds, without solid documented and enforced policies, standards and procedures (Policy Set), there is no real way you can have the culture of security necessary to achieve the company wide backing necessary to run an effective PCI project. The Policy Set is a corner-stone of your security program and should received its due.

6. No Standardisation

This is a very broad subject, and includes configuration standards, change control, monitoring, patch management, the SDLC, vulnerability management etc. The PCI DSS allows sampling of systems during validation, but this must be earned. Without standardisation, there can be no sampling as there are no systems created and maintained identically.

7. No Centralisation

How organisations manage often hundreds of devices without some form of centralised management is beyond me. I have to assume it’s not done well. The QSA also has a very hard time granting the privilege of sampling if you cannot show centrally HOW you keep the systems the same. There are plenty of tools out there, and the benefits of them go way beyond PCI compliance.

8. Not Knowing Where to Start

At first this may seem obvious, and perhaps a little redundant, but bear with me. I have had a lot of experience with this little roadblock, so I know just how difficult it can be to overcome. The answer – as it was for me – is simple; Ask someone. Your QSA should be able to take you all the way through this process relatively seamlessly, but if you don’t have one yet, ask someone who has already achieved compliance for their organisation. I personally know dozens of people who are more than happy to spend time with PCI novices and share their experience and guidance. This is one of the easiest roadblocks to overcome if you keep your ego or shyness out of play.

9. “But we’ve always done it this way!”

Perhaps the most irritating phrase in the English language – with the possible exception of “What are you thinking?”, especially for a consultant. The business wants things to stay the same, they want the same access they’ve always had, and they want the same data. The fact remains that the vast majority of business processes have very short shelf-lives, so they should be reviewed regularly, and access to in-scope systems or data justified. I’ve found that adding PCI compliance expenses to their cost centres tends to get their attention.

10. No Budget

Not much you can do about this one, but it’s certainly worth trying to re-iterate that the security controls should be in place anyway, and that they fall firmly in the good practices introduced in my The 6 Security Core Concepts.

I didn’t know how to blog until I asked my wife, and I have no idea how to read legal-ese so I ask my Sister. If you want to be PCI complaint, or even better, be secure AND PCI compliant, ask someone who’s done it.

[If you liked this article, please share! Want more like it, subscribe!]